

Cyber security certification mistakes rarely feel like mistakes at the time. They feel like progress another badge on LinkedIn, another line on the resume. The trouble usually shows up eighteen months later, when a recruiter asks why a candidate holds three certifications but still can’t explain how a SIEM correlates an alert, or why a CySA+ credential sits next to zero hands-on lab hours. In Australia’s security job market, where employers in Melbourne, Sydney, Brisbane, Adelaide, Perth and Canberra are all hiring against roughly the same shortlist of recognised certifications, getting the order wrong doesn’t just waste money. It can add one, two, even three years to the time it takes to land a genuine security role.
This guide walks through the seven cyber security certification mistakes we see most often in learners who come to us after already trying and stalling on their own, along with a practical roadmap for getting the sequence right the first time.
Why Cyber Security Certification Mistakes Cost You Years, Not Weeks
A wrong turn early in a certification plan compounds. Sit the wrong exam first and a candidate doesn’t just fail once they often fail twice, because the material assumed knowledge they didn’t have yet. Then comes re-study, re-booking, and a re-sit, usually months later once budget and confidence recover. Multiply that across two or three certifications and a career that should have taken twelve months from a standing start turns into three or four years of stop-start study with no job to show for it.
The Australian Cyber Security Centre has repeatedly pointed to a national shortage of certified, work-ready security professionals which is exactly why employers can afford to be selective about a candidate’s certification history rather than just the number of logos on a resume. A CompTIA Security+ certificate followed by a jump straight into an advanced governance exam, then a fall back to entry-level material, reads as directionless rather than ambitious. Recruiters in competitive markets like Sydney and Melbourne see hundreds of applications for every SOC analyst role; a certification path that doesn’t tell a coherent story is an easy one to scroll past.
Mistake #1 Skipping the Basics: The #1 Cyber Security Certification Mistake
The single most common cyber security certification mistake is skipping the foundation. Ambitious career-changers see senior job ads asking for CISSP or CISM and assume the fastest path is to sit that exam immediately. ISC2’s own CISSP certification requirements tell a different story: full certification generally requires several years of paid, hands-on experience across multiple security domains before the credential even makes sense.
Without that foundation, two things happen. First, the exam becomes a memory test rather than a demonstration of understanding, so the knowledge doesn’t stick or transfer to a real job. Second, even candidates who scrape a pass struggle in interviews, because hiring managers ask scenario-based questions that assume the practical exposure the candidate never had.
Why CompTIA Security+ Still Comes First
CompTIA itself positions Security+ as the natural entry point into a security career vendor-neutral, exam-aligned to entry-level roles, and built around the vocabulary (threats, vulnerabilities, risk, cryptography, identity and access management) that every later certification assumes you already know. Our CompTIA Security+ course is built around exactly that gap, with real lab time rather than pure theory, so graduates walk into a CySA+ course or a network security role already comfortable with the fundamentals.
Mistake #2 Choosing a Certification That Doesn’t Match the Job You Want
Not every cyber security certification leads to the same job, and treating them as interchangeable is a fast way to end up qualified for a role you don’t actually want. Someone aiming for a SOC analyst or threat-detection position needs a very different path to someone aiming for a governance, risk and compliance role five years down the track.
CompTIA vs CISSP vs CISM: Not Interchangeable
CompTIA Security+, CySA+ and PenTest+ are built around hands-on technical skills: detecting threats, analysing vulnerabilities, testing defences. CISSP leans toward security leadership and architecture across eight broad domains. CISM, from ISACA, focuses squarely on security management and governance rather than hands-on technical work. Picking CISM when the goal is a technical SOC role or picking PenTest+ when the goal is a CISO-track management career means starting the certification path over later. We’ve mapped the differences in detail in our CISSP vs CISM Australia comparison if you’re weighing those two directly.
Mistake #3 Memorising Answers Instead of Building Real Lab Skills
Brain dumps and question banks can get a candidate through an exam. They cannot get a candidate through a technical interview, a probation period, or a first real incident. This version of a cyber security certification mistake is especially costly because it’s invisible until the new hire is expected to actually configure a firewall rule, triage a SIEM alert, or write up a penetration test finding — and can’t.
Certifications like CompTIA CySA+ and CompTIA PenTest+ are performance-based by design, which means employers expect candidates to have logged real lab hours: analysing packet captures, running vulnerability scans, interpreting log data. Skipping the labs to save time on study doesn’t just risk exam failure it produces certified professionals who can’t do the job the certification claims they can do, and that gap surfaces in the first month on the job.
Mistake #4 Self-Study Without Exam-Aligned, Instructor-Led Training
Free video playlists and outdated exam dumps are tempting because they’re free, but exam blueprints change, vendors retire old material, and self-study rarely includes the structured lab environment that performance-based exams now require. Studying from content that’s even twelve months out of date is one of the more avoidable cyber security certification mistakes, because it usually isn’t obvious until exam day.
Instructor-led, exam-aligned training closes that gap two ways: the content stays current with the actual exam objectives, and a trainer can flag the specific areas where a given student is weak, rather than the student guessing. Our cyber security certification courses are delivered by working security practitioners across Melbourne, Sydney, Brisbane and Adelaide, with live virtual and in-house options for everywhere else, so the training matches the exam you’re actually about to sit.
Mistake #5 Letting Your Certification Lapse With No Renewal Plan
A certification earned three years ago and never renewed can do more damage to a resume than no certification at all it signals that the holder stopped keeping pace with a field that changes constantly. Most vendor certifications, from CompTIA to Microsoft to Palo Alto Networks, require continuing education credits or periodic renewal, and letting that lapse is a quiet but common mistake among professionals who assume the credential is a one-time achievement rather than an ongoing commitment.
Building a renewal plan at the same time as the original study plan knowing which CEUs count, when the renewal window opens, and what the next-tier certification should be avoids a scramble two or three years later.
Mistake #6 — Ignoring What Employers in Your City Are Actually Hiring For
Certification demand isn’t uniform across Australia, and training for the wrong regional market is an easy way to add months to a job search. Government and defence-adjacent employers around Canberra lean heavily on governance-focused, clearance-friendly certifications. Melbourne and Sydney carry the largest concentration of enterprise SOC and cloud security roles, where Microsoft’s AZ-500 and hands-on CompTIA credentials are frequently listed together in the same job ad. Brisbane and Perth have a heavier mix of critical infrastructure, mining and utilities employers, where a network security certification like Palo Alto’s PCNSA shows up more often than pure governance credentials. Adelaide’s defence and space-sector employers sit somewhere between the two.
None of this means a certification is useless outside its strongest region it means candidates who check local job ads before committing to a study plan avoid the common mistake of being well-qualified for a job market on the other side of the country.
Mistake #7 Treating Certification as a One-Off Instead of a Career Roadmap
The biggest structural cyber security certification mistake is planning one exam at a time instead of planning the whole sequence. A candidate who picks Security+ in isolation, passes, then spends three months deciding what comes next has already lost the momentum that made the first certification valuable. Certification pathways compound: each one should set up the next, with a clear view of where the sequence ends SOC analyst, penetration tester, cloud security engineer, or security manager.
We’ve mapped this out in detail in which certification to get first, second and third and in our broader cyber security certifications roadmap, alongside a look at which certifications actually pay the most in the Australian market and how Security+ compares to CySA+ for anyone deciding on a second step.
How to Fix These Cyber Security Certification Mistakes This Month
None of the seven mistakes above require starting over. Most can be corrected with a short planning conversation and a change in study approach, not a change in career.
- Map the end goal first SOC analyst, penetration tester, cloud security engineer or governance lead then work backward to the right first certification.
- Choose exam-aligned, instructor-led training over self-study PDFs, especially for performance-based exams like CySA+ and PenTest+.
- Book lab time deliberately, not as an afterthought, so the certification reflects real ability.
- Check job ads in your own city Melbourne, Sydney, Brisbane, Adelaide, Perth or Canberra before locking in a study plan.
- Set a renewal reminder the same week you pass the exam, not three years later.
If you’d rather talk it through than plan it alone, our team can map a certification pathway against your current experience and target role contact us for a free consultation, or browse the full course list to see what’s running near you.
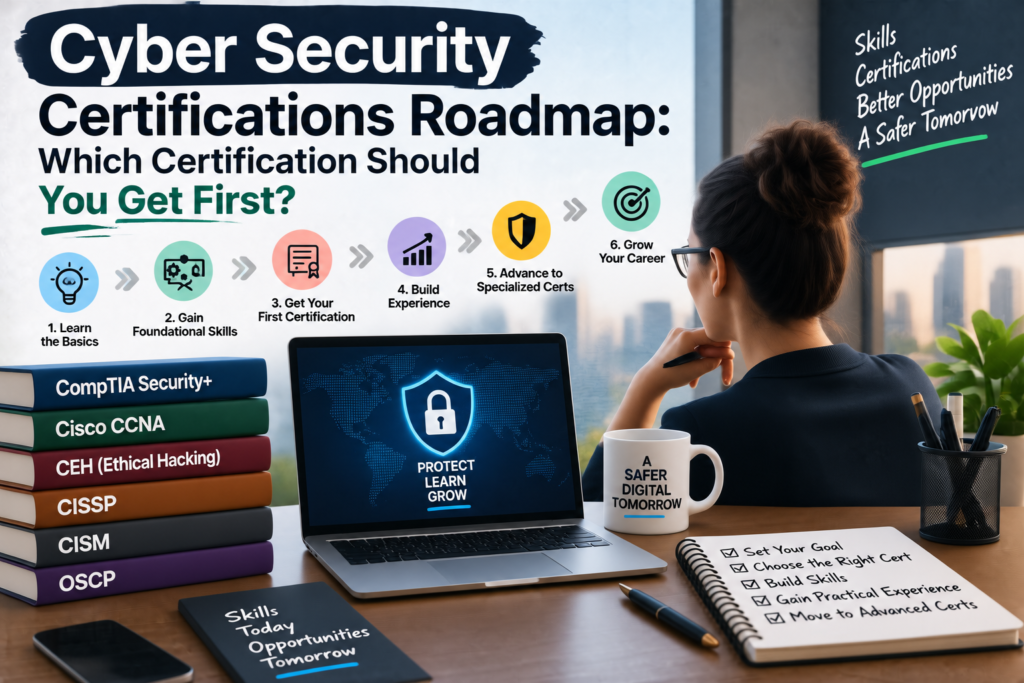
Cyber Security Certification Roadmap: A Quick-Reference Order
- Foundation: CompTIA Security+ the entry point for almost every security role.
- Specialise: CySA+ (threat detection / SOC), PenTest+ (offensive security), or PCNSA (network security).
- Cloud: Microsoft AZ-500 for Azure security engineering.
- Leadership: CISSP or CISM once real work experience sits behind you compare them in our CISSP vs CISM Australia
For the reasoning behind each step, see the full cyber security certifications roadmap and our list of the top 10 certifications Australian employers actually value.
FAQs About Cyber Security Certification Mistakes
What is the most common cyber security certification mistake?
Skipping the foundational certification usually CompTIA Security+ and attempting an advanced credential like CISSP before building the underlying knowledge and work experience it assumes.
Can a cyber security certification actually delay my career?
Yes. The wrong certification order, exam-only study with no labs, or training misaligned with local job demand can each add a year or more to the time it takes to land a security role, because the certification ends up not matching what employers in that field or region are hiring for.
Do I need work experience before sitting the CISSP exam?
ISC2 generally requires several years of relevant paid experience across specific security domains for full CISSP certification. Candidates without it can still sit the exam and hold Associate of ISC2 status while they gain the required experience.
How long does it realistically take to build a cyber security career from scratch?
With a clear certification roadmap and instructor-led training, most learners move from zero background to an entry-level security role in twelve to eighteen months. Without a roadmap, the same journey commonly stretches to three or four years.
Does the certification I choose matter more than the city I train in?
Both matter. The certification determines the skill set; the city determines which employers are actually hiring for that skill set right now which is why checking local demand in Melbourne, Sydney, Brisbane, Adelaide, Perth or Canberra before enrolling is worth the extra ten minutes.
Final Thoughts: Start Your Cyber Security Certification Journey the Right Way
Every one of these cyber security certification mistakes is avoidable with the right sequence, the right training format, and an honest look at what your local job market is hiring for. The professionals who move fastest aren’t necessarily the most technical they’re the ones who planned the whole pathway before sitting the first exam.
If you’re weighing up where to start, our team runs cyber security certification training across Melbourne, Sydney, Brisbane, Adelaide, Perth and Canberra, with live online options for everywhere else. Get in touch and we’ll help you build a certification roadmap that actually gets you hired not just certified.